For automotive, industrial and general-purpose MCUs and SoCs, CryptHSM® unifies cryptographic operations, key management, firmware authentication and authorized access within a single security domain. It has been adopted by multiple customers in volume-production products.
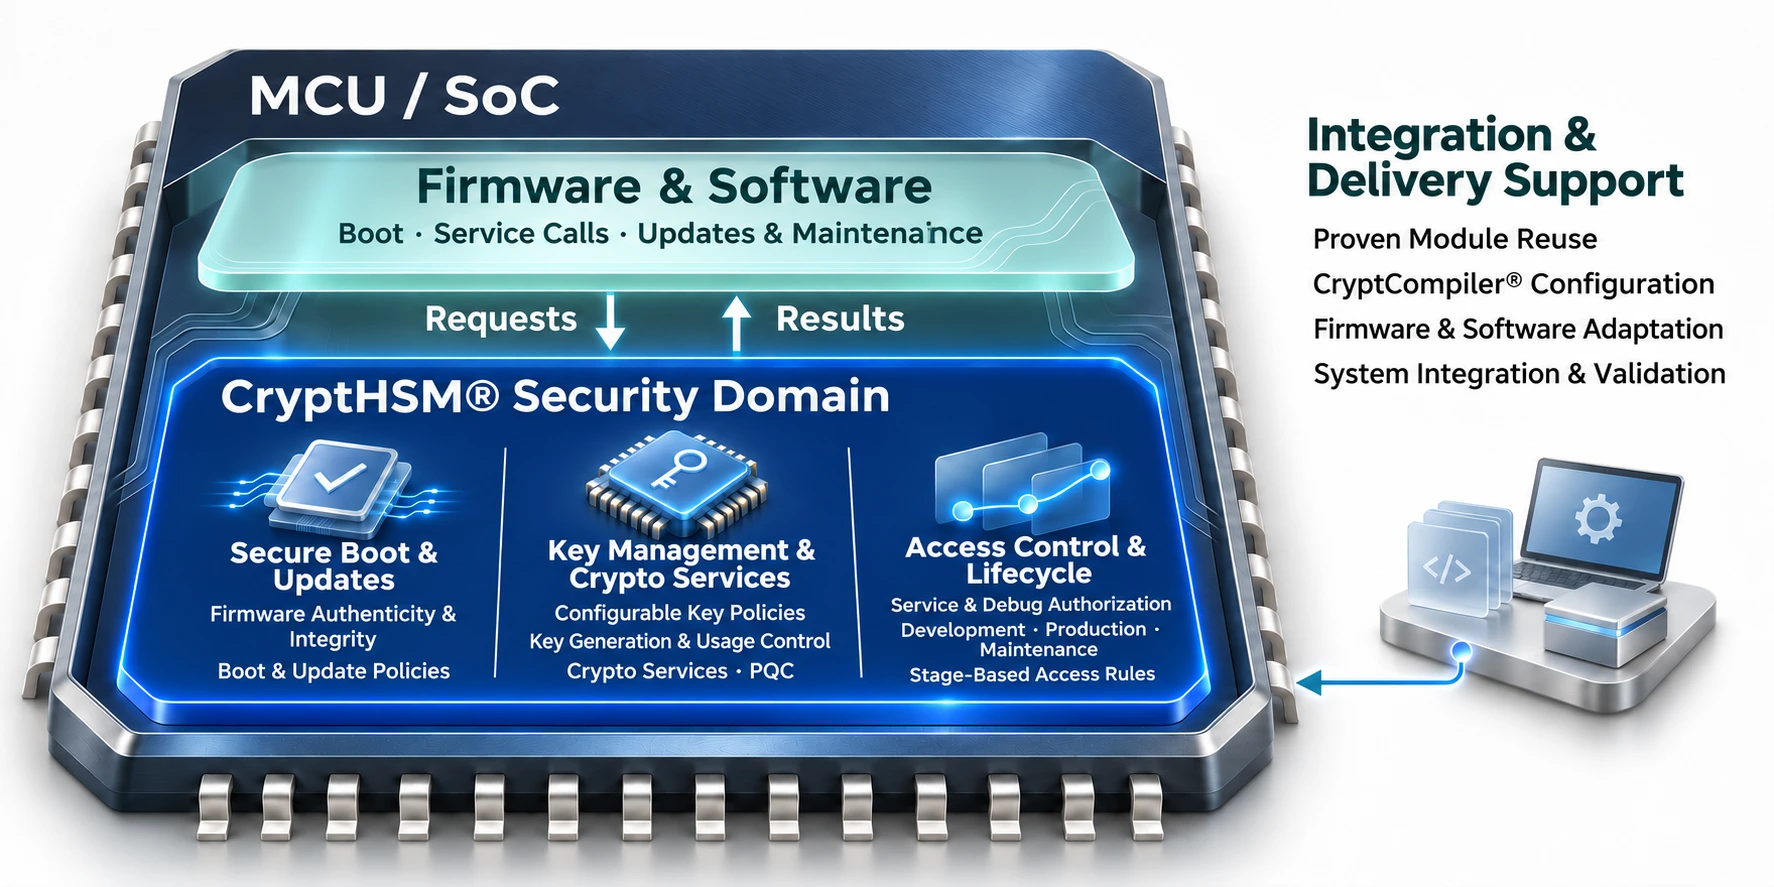
Core Security Capabilities
- Secure Boot & Updates
-
Verify firmware provenance and integrity, and integrate verification into boot, update and maintenance policies.
- Key Management & Cryptographic Services
-
Configurable key policies and cryptographic services control key generation, import, use and export, with optional integration of post-quantum cryptography.
- Access Control & Lifecycle
-
Configure authorization for cryptographic service calls and debug access across development, production and maintenance.
Automotive Applications
Security-domain integration for automotive MCUs and SoCs addresses AUTOSAR SHE and EVITA HSM Medium and Full architectures. It supports secure boot, firmware verification, authentication and automotive data protection, with optional physical-attack protection.
Integrated Hardware & Software Delivery
Reuse proven modules and use CryptCompiler® to explore algorithm IP configurations, reference PPA and physical-attack protection options. Supporting firmware and software can be adapted to platform interfaces and boot flows, with system integration, validation and technical support.
Evaluation & Technical Discussion
Share your target MCU or SoC, boot and update flows, key policies and required cryptographic services. We will arrange a technical discussion.
